
Question 1
Choose 1
An administrator set up a new user account called "test". However, the user is unable to change their
password. Given the following output:
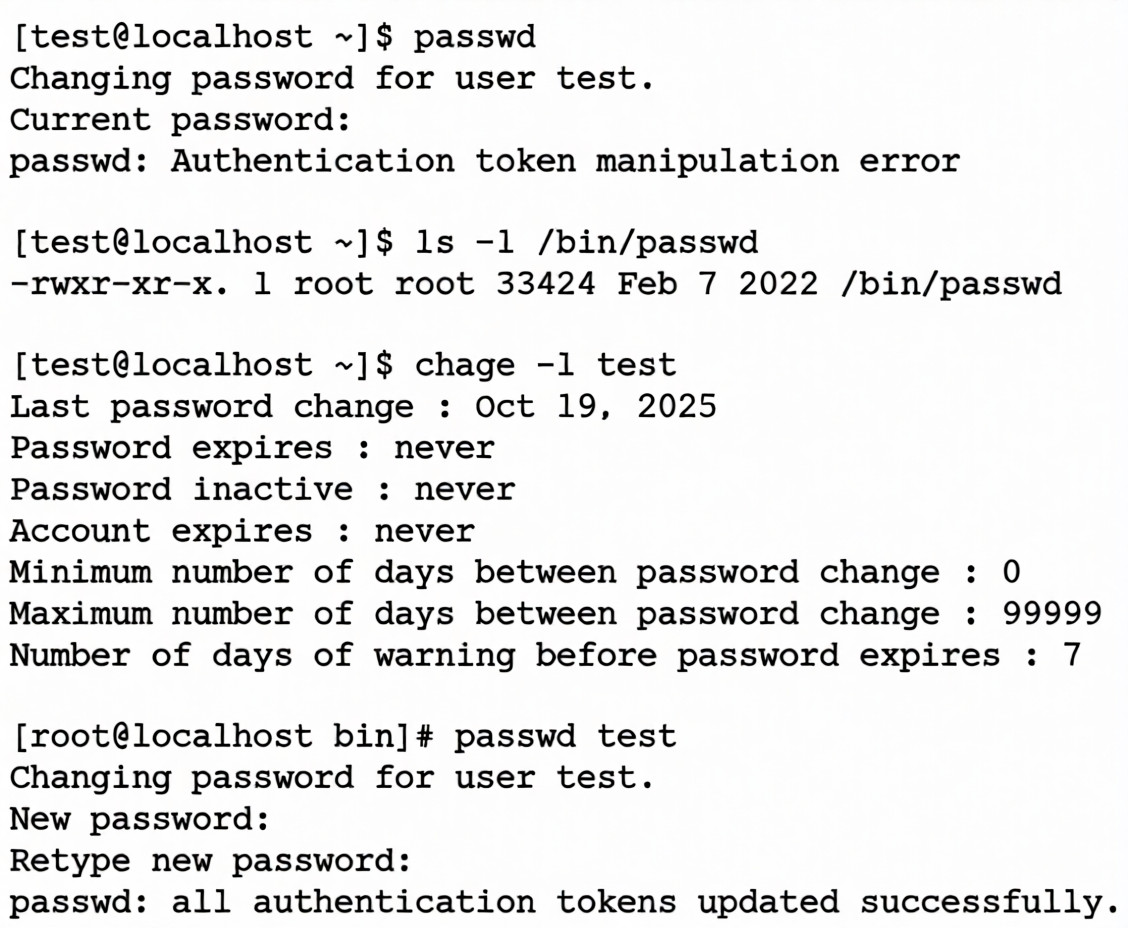
Which of the following is the most likely cause of this issue?
Which of the following is the most likely cause of this issue?
Correct answer:
A. The SUID bit is missing on the /bin/passwd file.
Explanation:
The error message:
passwd: Authentication token manipulation error
usually indicates that the passwd binary cannot update the shadow password file because it lacks the necessary privileges.
Normally, /bin/passwd should be owned by root and have the SUID bit set (-rwsr-xr-x), allowing regular users to run it with root privileges for password changes.
In the output provided, /bin/passwd is shown as:
-rwxr-xr-x. 1 root root ...
→ Notice the missing s in the permissions. This confirms the SUID bit is not set, preventing the user test from changing their password.
Why the Other Options Are Wrong
The password provided by the user "test" does not meet complexity requirements: The error would be different (e.g., "BAD PASSWORD").
The user "test" already changed the password today: The chage output shows minimum days between changes = 0, so this is not a restriction.
The password has been disabled for user "test": The account is active, and root was able to change the password successfully.
Reference:
Linux man page: man passwd → Requires SUID to update /etc/shadow.
CompTIA Linux+ XK0-006 Exam Objectives: User and Group Management (Domain: Security).
The error message:
passwd: Authentication token manipulation error
usually indicates that the passwd binary cannot update the shadow password file because it lacks the necessary privileges.
Normally, /bin/passwd should be owned by root and have the SUID bit set (-rwsr-xr-x), allowing regular users to run it with root privileges for password changes.
In the output provided, /bin/passwd is shown as:
-rwxr-xr-x. 1 root root ...
→ Notice the missing s in the permissions. This confirms the SUID bit is not set, preventing the user test from changing their password.
Why the Other Options Are Wrong
The password provided by the user "test" does not meet complexity requirements: The error would be different (e.g., "BAD PASSWORD").
The user "test" already changed the password today: The chage output shows minimum days between changes = 0, so this is not a restriction.
The password has been disabled for user "test": The account is active, and root was able to change the password successfully.
Reference:
Linux man page: man passwd → Requires SUID to update /etc/shadow.
CompTIA Linux+ XK0-006 Exam Objectives: User and Group Management (Domain: Security).